Star Blizzard refines phishing and malware delivery with the RedFlick technique
Since January 2026, Microsoft has observed Russian state threat actor Star Blizzard evolve their detection evasion capabilities through larg...


Since January 2026, Microsoft has observed Russian state threat actor Star Blizzard evolve their detection evasion capabilities through larg...
As threat actors increasingly use AI to accelerate and develop cyberattacks, enterprise defenders need to rely on both AI and a critical def...
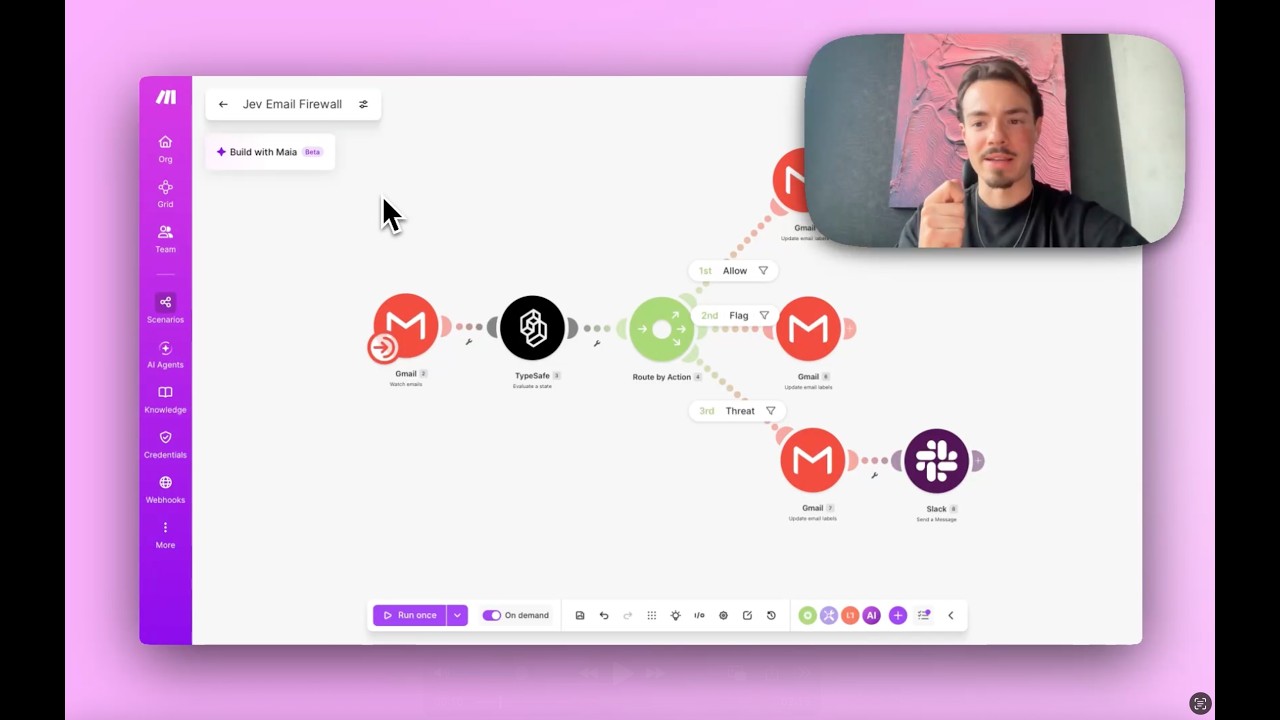
Learn how to build an automated email threat-detection system in Make using Jev, a new decision model from TypeSafe. Unlike a typical LLM, J...

Agents you can coach: how Asana builds human-agent teams with Claude 🔗 Claude Blog https://claude.com/blog/agents-you-can-coach-how-asana...

EvilTokens has quickly become one of the top PhaaS platforms, enabling device code phishing attacks through AI-assisted lures, automated inf...

Microsoft Threat Intelligence identified NeedyMantis, a modular post-compromise malware framework used in targeted intrusions that combines ...
Edy Massih uses Gemini to transform regular recipes into massive catering spreads, automate grocery orders, and adapt menus for dietary rest...

OpenAI's security experts explain why every organization needs a cyber defence factory, and how to build it with Daybreak. 🔗 OpenAI h...

It’s a result of metallurgy, but circular silicon wafers are also the best shape to ensure uniformity in the chip production process. 🔗 IBM...

La ley te exige seguridad y confidencialidad de datos. No es solo tecnología, incluye contratos, procesos y capacitación. Demuestra que toma...
Presento mi nuevo playbook de más de 550 páginas para crear, analizar, automatizar y auditar planillas empresariales con inteligencia artifi...